Whoa! I remember the first time I wrote down a seed phrase and felt like I’d secured the vault. My instinct said that paper in a safe was old-school but reliable. Initially I thought that was enough, but then a subtle paranoia crept in—what if the paper fades, or someone finds it, or I misplace it during a move? On one hand a written seed is simple and offline, though actually the human part of storage makes it fragile in ways hardware can avoid.
Seriously? The mess of UX and security around private keys still surprises me. People treat mnemonic phrases like talismans, and that scares me a little. I’ll be honest: somethin’ about a string of words taped under a desk bugs me. On the flip side, hardware alternatives are not magic, and they too carry trade-offs that most guides gloss over. My goal here is pragmatic—help you think in terms of threat models, not just shiny solutions.
Here’s the thing. When we talk about private keys and seed phrase alternatives, we are really talking about who can access value and under what conditions. My experience with cold storage setups taught me that convenience and safety pull in opposite directions most of the time. So I try to balance practical deployments (what people will actually use) against high-assurance methods (what experts would recommend). That tension matters because most losses happen from human error or social-engineered attacks, not from cryptographic failure.
Hmm… pause for a sec. Imagine losing access to a legacy account because you trusted a third-party custodian without the right checks. It happens. People get phished, they miscopy words, or they forget the tiny specifics that make a backup valid. Initially I underestimated how many ways a seed phrase can be compromised in the wild. Actually, wait—let me rephrase that: I underestimated how often user behavior, not tech, becomes the weakest link.
Okay, so check this out—there are alternatives that trade the fragile paper for durable devices and human-friendly recovery flows. Some smartcards store keys in a secure element and never reveal private keys externally, which reduces exposure to malware. Others use Shamir-style splitting (secret sharing) to distribute risk across pieces so no single loss ruins everything. Multisig setups distribute control across devices or people, which raises complexity but also resilience. And then there are hybrid approaches that mix these ideas according to your needs.
How to think about protecting private keys
Start with threat modeling. Who are you protecting against—thieves, coercion, accidental loss, state actors? Short answers are useless here. My gut reaction used to be “protect against everyone,” which is paralyzing. On the other hand, designing for every extreme can make routine use impossible, so target the most realistic threats first. For most users in the US, that means guarding against phishing, malware, theft, and human forgetfulness.
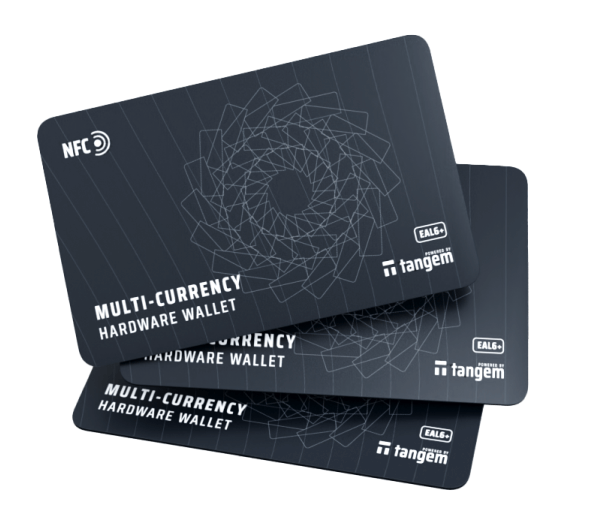
My instinct said hardware is the obvious answer. And to an extent it is. Hardware wallets containing a secure element—little chips that resist tampering and never expose the private key—dramatically lower the attack surface compared to hot wallets. But hardware devices vary; some are tiny USB sticks, others are cards you tap to a phone. I’m biased, but the smartcard form factor has real UX advantages; it’s familiar, portable, and integrates well with phones. Check a practical example in the wild like tangem, which uses a card-based secure element model that feels like carrying a credit card with cryptographic superpowers.
On the technical side: private keys should ideally never leave the secure element in plain text. Instead, devices sign transactions internally and return only signatures. That reduces the chance that a laptop infected with malware can exfiltrate your key. But there’s more—recovery processes need thought. A device that is too rigid about recovery can brick access if the owner loses it, while a device that is too loose risks social-engineered recovery. So design and human factors collide again.
Whoa! Another thing: the “seed phrase” mental model is terrible for many people. It pushes a single point of failure into your life. You’re told to write down 12 or 24 words and guard them like gold. That works for some, but many either make careless copies or end up storing them in digital notes, which is effectively handing keys to attackers. There are alternatives, though they require discipline and a small learning curve. For example, distributing secrets (Shamir) can be as simple as splitting into three pieces and storing them in different safe locations, or as formal as a multisig with trusted friends or services.
Hmm… I should add a caveat: every split increases operational complexity. Initially I thought more splits = more safety, but then realized diminishing returns and new failure modes. If one of three shares is lost, you might still recover, but if you mismanage the process you could lose everything. On the balance, share-splitting suits people who want geographically distributed resilience and who are comfortable with the bookkeeping that comes with it.
Comparing common approaches — blunt overview
Short: paper seed is cheap but fragile. Medium: hardware secure elements are resilient and broadly compatible. Long: multisig and secret sharing provide robustness through distribution, but require more coordination and have higher operational overhead, especially for less technical users who might panic during an emergency. The trick is picking the right combination for your life stage and crypto holdings.
Here’s another real-world wrinkle—recovery friction. If you’re managing small amounts, a complex multisig is overkill. If you hold serious value, you should invest time and possibly professional advice to architect a robust solution. My own setups evolved: early on I used simple cold storage and a paper backup. Later I moved to cards and multisig because the administrative and theft risks scaled with my holdings. That transition wasn’t overnight; it came after a few close calls and some sleepless nights.
Really? Physical coercion is a threat people rarely plan for. If someone can force you to reveal a seed, then all the cryptography in the world won’t help. There are techniques—plausible deniability wallets, duress phrases, or legal structures—but they come with trade-offs and ethical complexity. On one hand you can hide access behind plausible decoys, though actually relying on deception carries its own risks and moral questions.
Finally, consider lifecycle management. Keys aren’t static; devices age, firmware updates happen, and relationships change. A recovery plan that worked when you set up the wallet might be useless years later if your trusted co-signer moved, passed away, or changed contact details. So design with change in mind, and periodically test recovery without risking funds (use testnets or small amounts first).
Practical patterns I recommend (with caveats)
First, separate everyday access from emergency recovery. Keep a small hot- or warm-wallet for routine transactions, and use a hardened cold setup for long-term holdings. That’s simple to say, though behaviorally it’s harder to maintain. Second, use hardware with a secure element that never exposes private keys, and prefer models with simple, audited recovery options. Third, consider distributing recovery across devices and trusted parties if you have meaningful holdings.
I’m not 100% sure which exact product fits everyone. But choose well-audited solutions and avoid one-off DIY electronics unless you are a seasoned hardware engineer. I’m biased toward tangible, offline devices that feel like everyday objects—cards, keys, or small tokens—because people actually carry and interact with them. Oh, and by the way… label things clearly but not too clearly; avoid leaving a note that screams “crypto seed!”
Something felt off about the handshake between UX and security in many wallet setups I tested. The most secure systems become useless if users can’t operate them reliably, and the easiest systems are often the least secure. So pick a middle way: enough security to defend against common threats, plus a recovery workflow you can test and trust.
FAQ
Can I replace my seed phrase entirely with a smartcard or hardware token?
You can, in many cases. A smartcard that holds the private key and never exposes it externally acts as a seed-less solution by design; it stores the secret inside a secure element and performs signatures internally. That removes the need to memorize or write down mnemonic words, but you must plan for loss or damage. Backup strategies include owning a second card, using multisig, or employing secret sharing. No single approach is universally best; choose based on your threat model and willingness to manage complexity.
How do I pick between multisig and secret sharing?
Multisig is about requiring multiple independent approvals for spending, often across different devices or people; secret sharing splits a single secret into pieces that must be recombined. Use multisig when you want operational separation (for example, different devices in different locations), and secret sharing when you favor physical distribution without constant co-signers. Both increase resilience but also increase administrative overhead—test your recovery flow before large transfers.
Are smartcards like Tangem safe?
Smartcards using secure elements offer strong protection against remote malware and are convenient for phone-based use. Implementation quality and ecosystem matter, and audits are crucial. If you prefer a card form-factor, look at reviews, audits, and community feedback. I carry cards in my pocket sometimes because they blend into life more naturally than bulky devices, but that convenience requires a deliberate backup plan.